7. Security (IDS/IPS)
7.1 Overview
The Security page controls Suricata, an intrusion detection and prevention engine, inspecting traffic against a continuously-updated set of threat signatures.
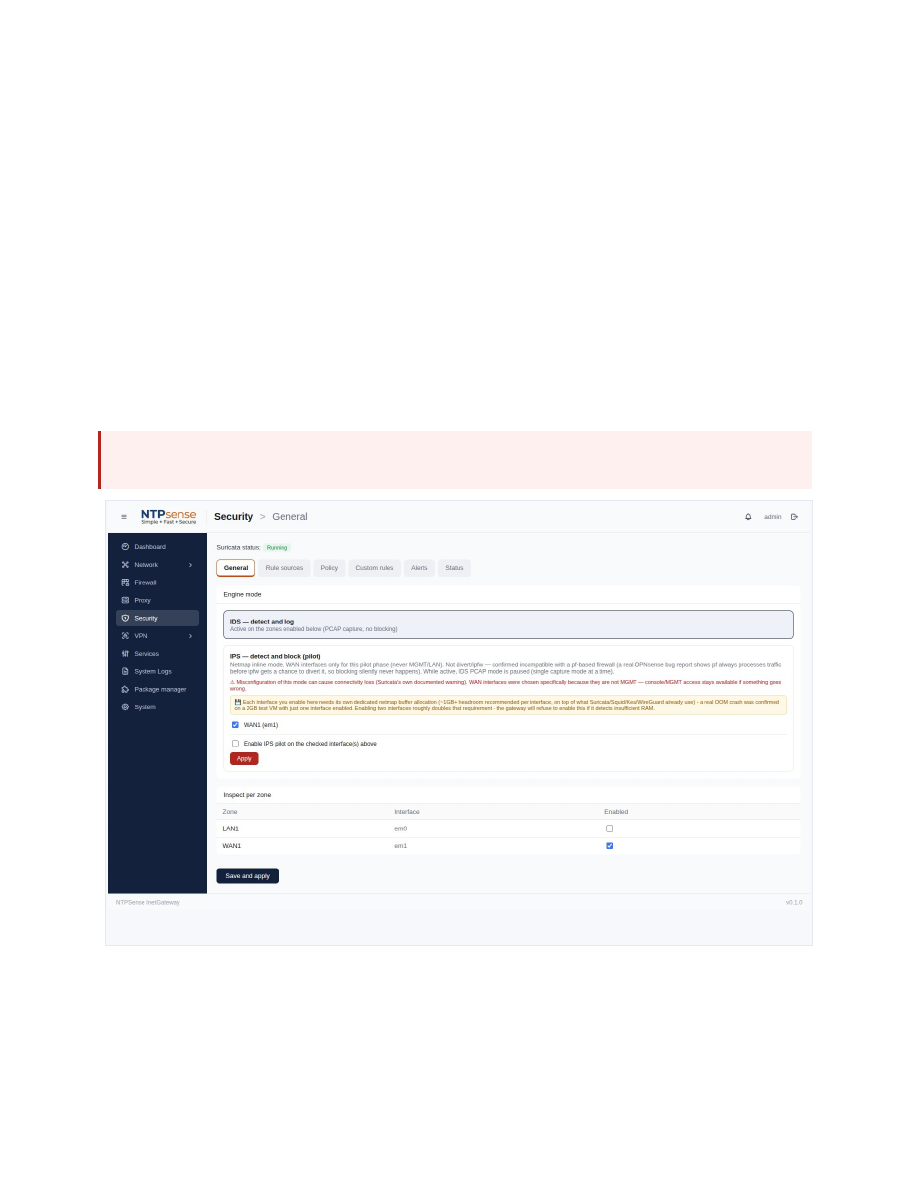 Security page overview
7.2 Engine Mode: IDS vs. IPS
- IDS (detect and log) — the safer default, no risk of disrupting connectivity.
- IPS pilot (detect and block) — active inline on WAN interfaces only, never LAN or the management path.
Warning
Enabling IPS pilot mode requires roughly 1 GB or more of free RAM per interface. The gateway refuses to enable it if it detects insufficient memory.
7.3 Rule Sources
Detection signatures come from ET Open, OISF Traffic ID (default), and optionally Abuse.ch SSL/JA3 + URLhaus.
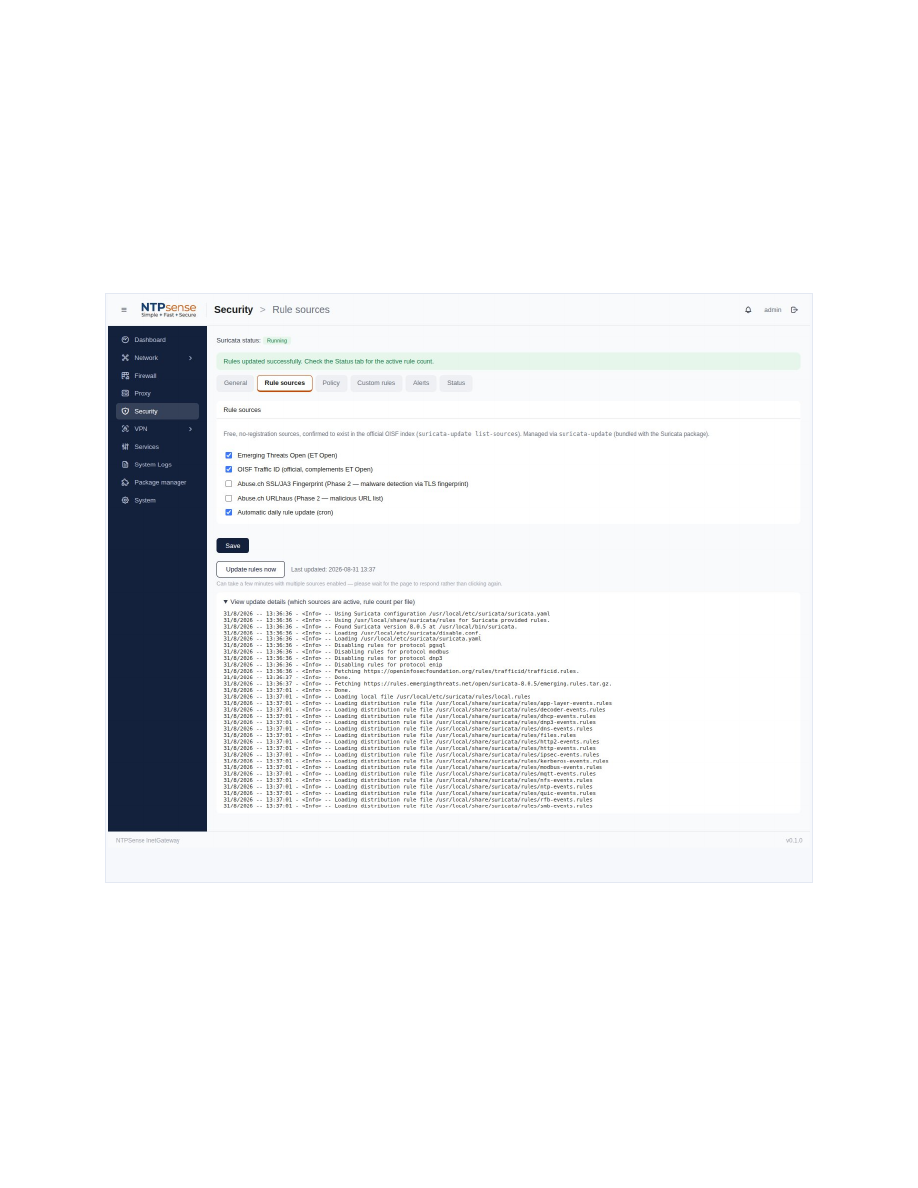 Rule sources tab
7.4 Policy
Disable noisy rule categories (chat apps, online games, etc.) — takes effect after the next rule update.
7.5 Custom Rules
Add your own Suricata signatures directly. Rules are validated automatically — a syntax error keeps the previous working ruleset active rather than taking detection offline.
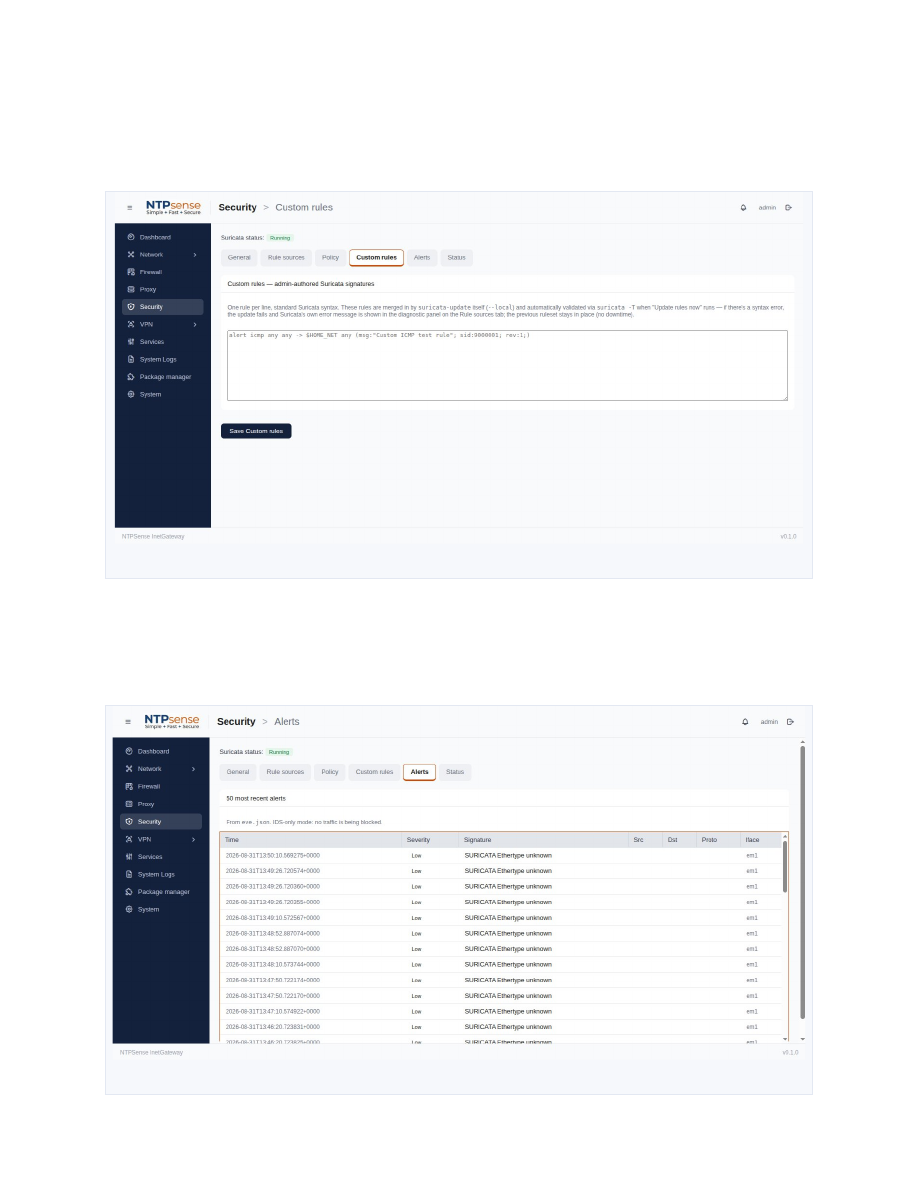 Custom rules editor
7.6 Alerts
The 50 most recent detections: timestamp, severity, matched signature, and source/destination.